Google's Threat Intelligence Group (GTIG) published a report this week with a blunt title: "Agentic Threat Activity Crosses a Significant Threshold." According to SiliconANGLE's coverage, it describes the first observed case of an AI framework running with no human in the loop to turn security patches into exploits.
What exploit_agent actually does
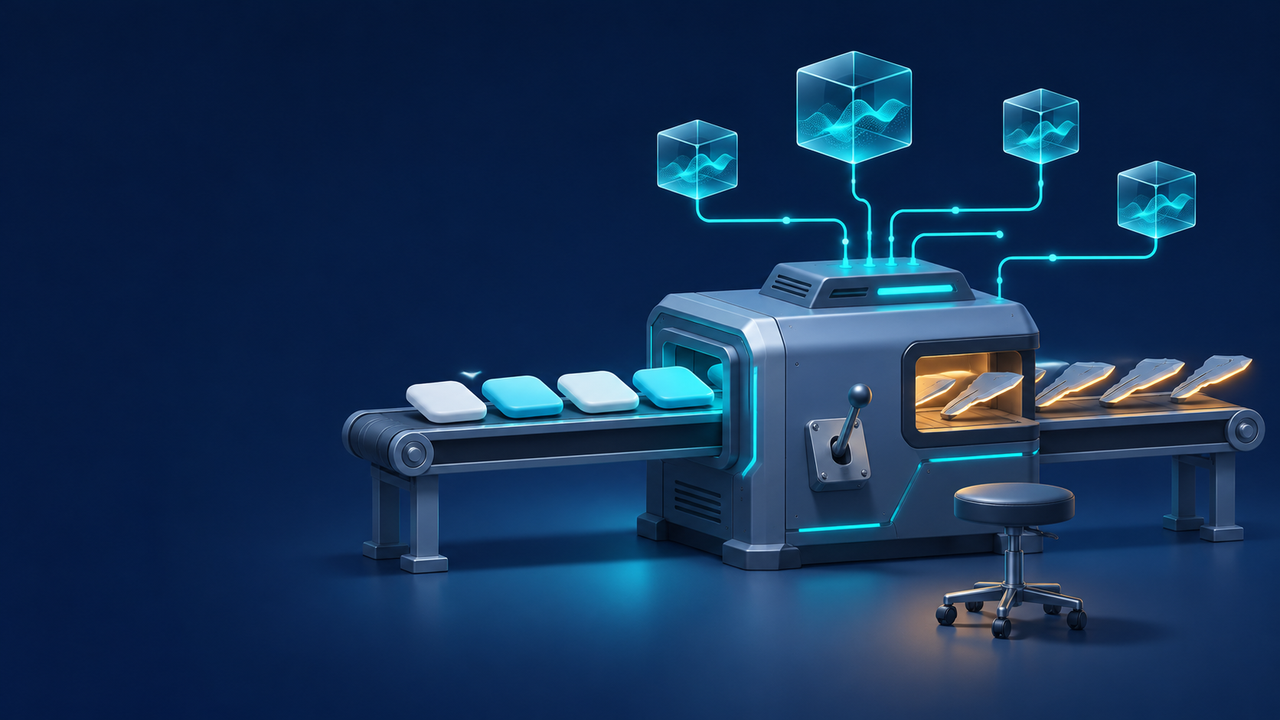
The framework, called exploit_agent, turned up on an exposed staging server wired into several frontier and locally hosted language models. Per GTIG, it continuously compares popular web application code before and after each patch announcement, drafts an exploit for any likely flaw, and runs it automatically. Stolen victim data and scripts for brute-forcing and installing webshells sat on the same server, and victim telemetry pointed to French media, entertainment and education sites.
Why patches are the new target
GTIG's logic is simple: a patched flaw leaves finite source material to analyze, so pointing a model at known "n-day" bugs may be more efficient than hunting for brand-new zero-days. The report cites two PaperCut print server flaws exploited in late August, where researchers used language models to generate working exploits within a day of disclosure, and a campaign tracked by GreyNoise that reached domain administrator within minutes at one foothold.
The silver lining, per the report: unrestricted autonomous execution leaves a noisy forensic trail, so these tools are currently easier to detect.
What it means for you
If you work in IT, security or run any team's tooling, "we'll patch next week" just got more expensive as a policy. For everyone else, the practical takeaway is to turn on automatic updates for your phone, laptop and the apps you rely on for work. The same report notes attackers using a modified Claude Code settings file to plant a backdoor, a reminder that developer tools and config files are now part of the attack surface.
Timing is everything, and in security it is now measured in hours. Source: SiliconANGLE, reporting on Google's GTIG report.